| ITSupportPanel · Authentication |
Authenticate users on the agent
Authentication links an Active Directory (AD) user or a local user with a PSA contact of the client the agent is already activated for. It can be done by the end user (options 1 and 2) or by the MSP, with no end-user involvement (options 3 and 4).
| Logging the first ticket Recommended |
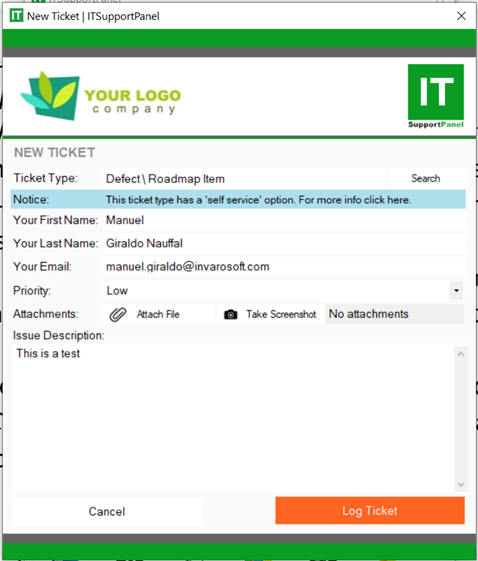
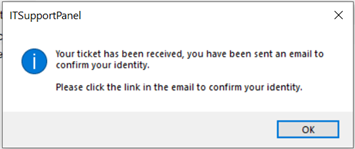
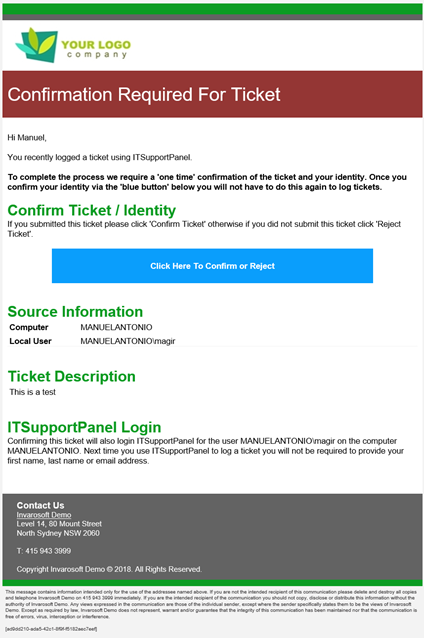
When the user logs a ticket from an activated agent that hasn't been authenticated yet, the app asks for their first name, last name and email.
- If the email matches a PSA contact, the AD or local user is linked to that contact.
- If there's no match, but the email domain matches the client's most common domain, Invarosoft creates the contact in the PSA.
| Registering |
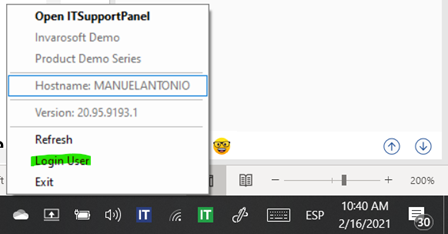
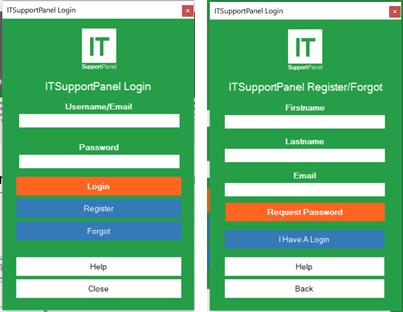
The user right-clicks the IT icon in the task tray and selects Login.
Then they select Register, enter their first name, last name and email, and click Request password. We send them the credentials to authenticate.
| Manual assignment |
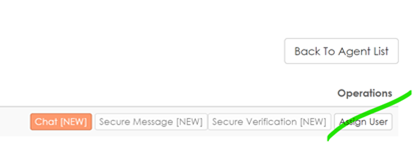
Once an agent is activated, it appears in your agent list in the Invarosoft Portal. Find the device and click Manage.

You'll see a list of each AD or local user on that device. Click Assign user to match a user with an existing PSA contact.
For the full walkthrough, see How to Authenticate a User.
| AD Harvester Fully automated |
If the client has an on-premise Active Directory with a single organizational unit, and its users have valid first name, last name and email values, you can automate authentication by installing AD Harvester on the server. It's available for non-trial partners.
Set it up |
Watch the video tutorial to set it up:
Can't see the video? Watch it on YouTube.
Was this article helpful?
That’s Great!
Thank you for your feedback
Sorry! We couldn't be helpful
Thank you for your feedback
Feedback sent
We appreciate your effort and will try to fix the article